The authorities advise against paying ransom, recommending immediate reports about any incident, coupled with information security best practices to respond to this threat.
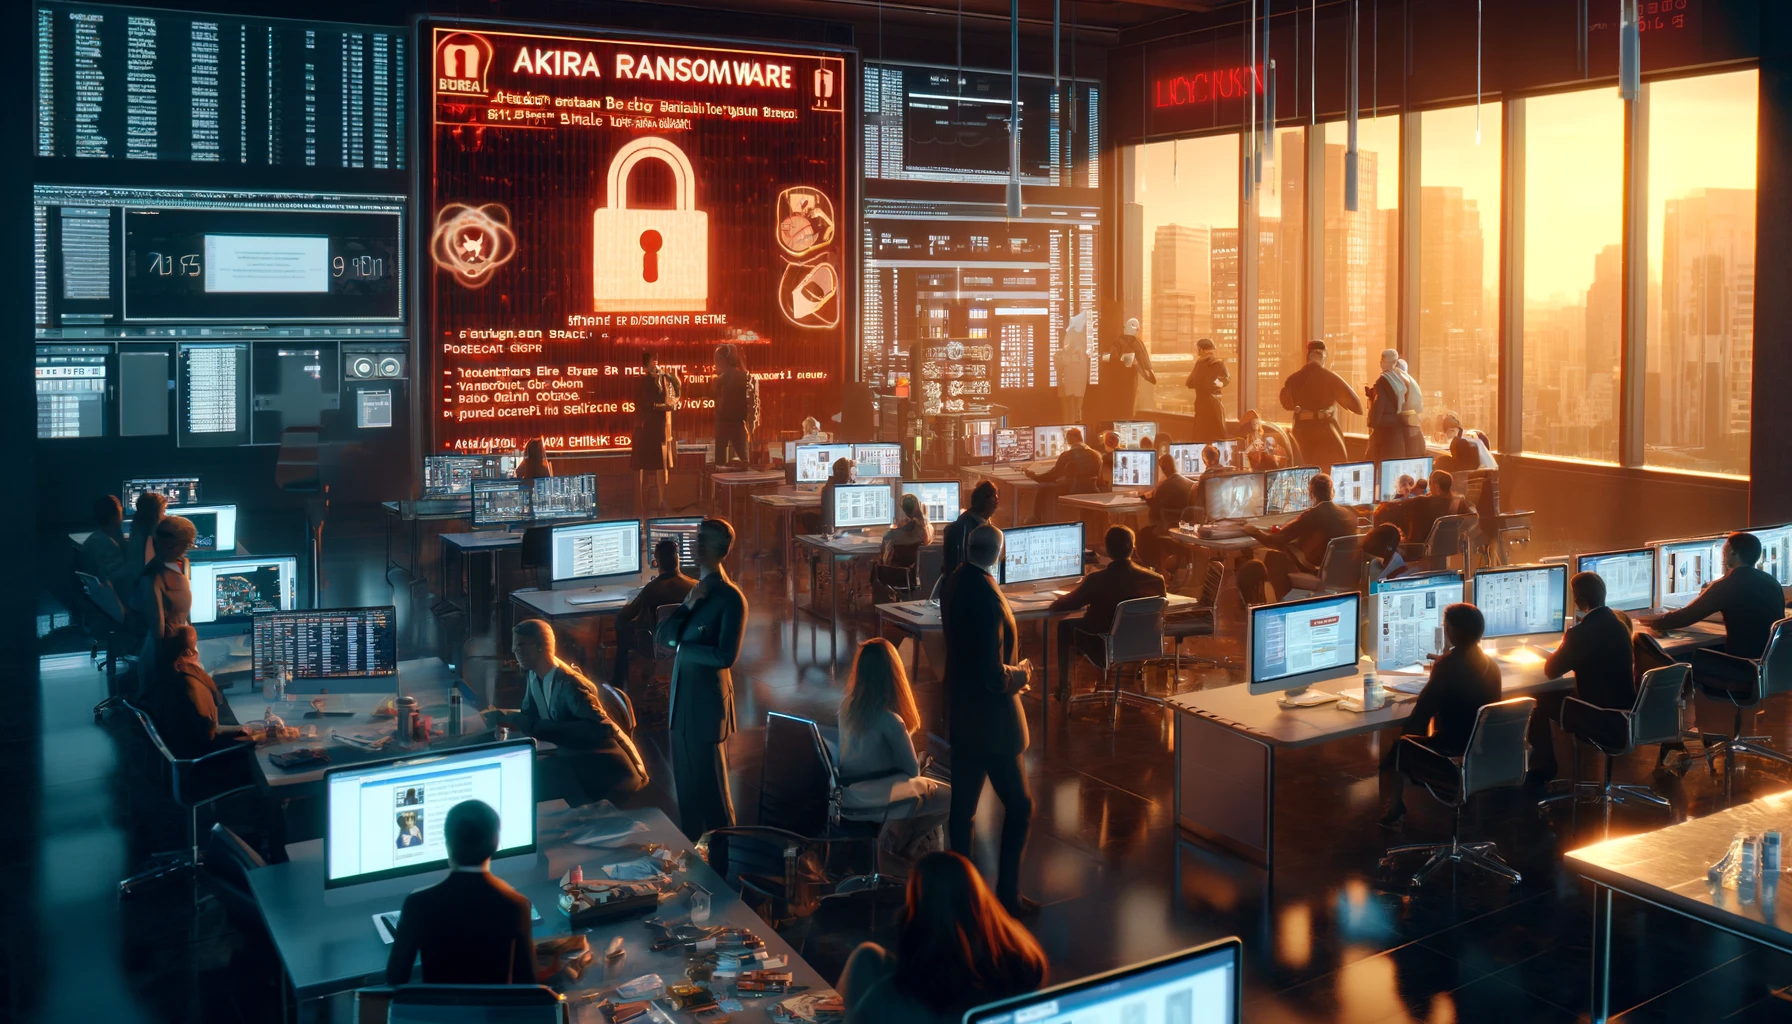
Local authorities from Singapore have issued a joint advisory warning businesses of the threats posed by Akira, a ransomware variant that has stolen $42 million—most of which is demanded in crypto—from over 250 organizations across North America, Europe, and Australia, all within a year.
According to the advisory, the ransomware group behind Akira is now actively targeting businesses in Singapore.
“The Akira threat group operates as an affiliate-based ransomware threat group, targeting both Windows and Linux systems under a “ransomware-as-a-service” (RaaS) model,” the police statement reads.
The Cyber Security Agency of Singapore (CSA), the Singapore Police Force (SPF), and the Personal Data Protection Commission (PDPC) have recently received several complaints from victims of the cyberattack. Investigations conducted by the United States Federal Bureau of Investigation (FBI) found that Akira ransomware primarily targets businesses and critical infrastructure entities.
Akira members usually demand crypto from victims in exchange for regaining control of their computer systems and internal data. In response, Singaporean authorities have advised businesses not to make payments, as it does not guarantee that the data will be decrypted or that threat actors will not publish the compromised data. Moreover, malicious entities may attempt another attack in hopes of receiving more ransom.
The FBI found that Akira never contacts the victims and expects them to reach out. To mitigate the threat, authorities recommend implementing a recovery plan, multifactor authentication (MFA), filtering network traffic, disabling unused ports and hyperlinks, and system-wide encryption.